Meta has a big ambition for Muse, its new personal AI agent. The company wants to give the software enough access to actually get things done for you.
That could mean booking travel, filling out forms, making purchases, working with email, remembering personal preferences and connecting with services people already use. In addition, Meta says Muse can continue working in the background and return when it needs approval or has something useful to report.
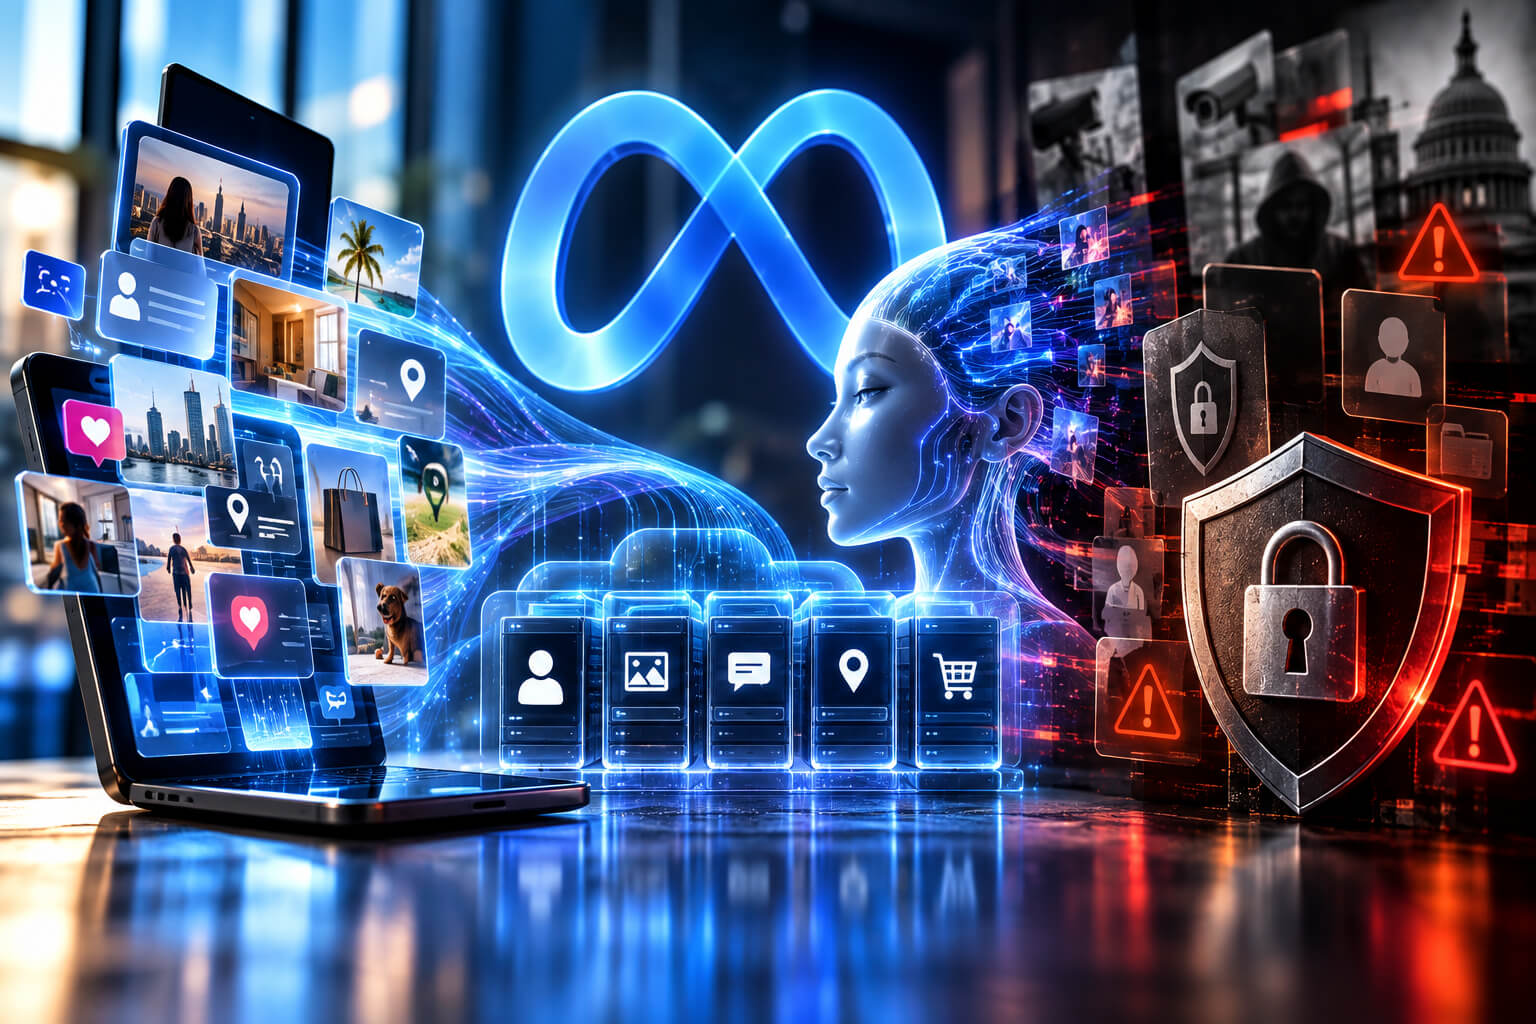
There is an obvious catch. An AI agent becomes considerably more useful when it knows more about the person using it. That can mean handing over access to information people normally protect carefully. This may include accounts, conversations, credentials, shopping habits and potentially financial or other sensitive information.
Meta knows this is going to be a difficult sell. The company has therefore put privacy and security unusually close to the center of its Muse pitch. However, the technology arrives with baggage that no security architecture can simply erase. This is Meta’s long record of privacy investigations, regulatory penalties, breaches and disputes over how Facebook and its other platforms have handled personal information.
That makes Muse more than an AI product launch. It is also a test of whether Meta can persuade people to trust an AI agent with a much deeper view of their digital lives.
Muse Needs More Than a Chat History
Muse isn’t being positioned as another chatbot sitting in a browser tab. Instead, Meta describes it as a personal agent capable of carrying out work rather than simply generating answers. The agent can operate a browser, complete forms and handle tasks such as travel bookings. Moreover, Meta says the agent can remember information that matters to a user and use those details later when making suggestions.
That difference matters because traditional social platforms largely wait for people to open an app and interact with content. An agent needs permission to move between services, retrieve information and sometimes act on the user’s behalf. The usefulness rises with access. So does the sensitivity of what sits behind that access.
Meta is already expanding that model. At Connect 2026, the company announced that Muse would come to its AI glasses. In this way, the agent can respond to what a wearer is looking at and potentially take action without the user having to describe the scene manually.
Meta Built a Security Architecture Around Muse
Meta’s answer is Muse Secure VM, a dedicated virtual machine designed to isolate an individual’s agent and the information connected to it. According to Meta, credentials placed into secure storage can be used by Muse without the agent itself seeing passwords or payment details. Additionally, a separate Sentinel agent checks activity before Muse communicates with the internet, while sensitive actions such as sending an email or completing a purchase require user approval.
Users can choose which services Muse connects with, adjust permissions and disconnect services later. Meta also says conversations and information stored inside a person’s Muse virtual machine aren’t shared with its advertising systems. Furthermore, users can opt out of having their Muse interactions used to train Meta’s AI models.
A stronger privacy layer is planned as well. Meta says Muse Confidential VM will encrypt the entire virtual machine using a key held by the user. The architecture is intended to prevent even Meta from accessing the person’s Muse data and conversations. Technically, that is a much more serious privacy proposition than simply asking users to trust a policy page.
Whether people trust the company operating it is another question.
Meta’s Privacy Record Is Difficult to Separate From Muse
The skepticism around Meta and personal data didn’t appear with generative AI. In 2019, Facebook agreed to a $5 billion Federal Trade Commission penalty to settle charges that it violated a 2012 FTC privacy order. The settlement also imposed new privacy restrictions and changes to Facebook’s corporate oversight structure.
European regulators have taken major action too. Ireland’s Data Protection Commission imposed a €1.2 billion fine on Meta in 2023 following an investigation into transfers of Facebook user data from the EU and European Economic Area to the United States. The regulator found that Meta had infringed Article 46(1) of the GDPR under the circumstances examined in the case.
Another case followed in 2024. Ireland’s DPC fined Meta €251 million after investigating a 2018 Facebook data breach affecting approximately 29 million accounts globally, including around three million in the EU and EEA. In the United States, Meta also agreed to pay $1.4 billion to Texas in 2024 to settle a lawsuit concerning the capture and use of biometric data through Facebook’s facial-recognition technology.
Those cases involved different technologies, legal questions and periods in Meta’s history. They don’t establish that Muse itself mishandles user information. However, they do explain why Meta is spending so much effort explaining how Muse handles data before asking people to connect more of it.
AI Agents Change the Privacy Equation
Agentic AI creates a different relationship between a platform and personal information. A social network can learn from what somebody posts, watches, clicks or likes. But a capable personal agent could potentially work across far more intimate parts of daily life because users deliberately give it permission to do so.
Muse is designed around exactly that idea. The agent can remember details, interact with connected services and carry out tasks. Meta says people remain in control of which apps are connected and what level of access Muse receives. These permissions become increasingly important as agents gain the ability to perform more consequential actions.
A technically secure system still needs users to understand what they’re authorizing, what information remains available to the agent, when an external service becomes involved and how easily that access can be withdrawn. The challenge isn’t merely preventing hackers from getting inside. Instead, it is making increasingly powerful permissions understandable enough that ordinary users can make informed decisions about them.
Meta Has to Earn Trust While Building the Product
Meta clearly understands that privacy could determine how far Muse goes. Its launch material doesn’t treat security as a footnote. Rather, dedicated virtual machines, isolated credential storage, action approvals, audit trails and the planned confidential computing layer form part of the core product story.
Still, software architecture and corporate trust are two different problems. Muse may ultimately demonstrate that Meta can operate a deeply personalized AI agent while keeping sensitive information isolated. Its security model deserves to be judged on how it works in practice. This should not be based solely on controversies attached to older Facebook products.
But Meta doesn’t get to launch from a blank page either. Years of regulatory action mean users have plenty of reasons to examine the details before connecting email, accounts, payments and other personal information to a Meta-operated agent.
For Muse, that may become one of the most important product tests of all.
Sources
Social Media Today — Can Meta Be Trusted With User Data to Power Its AI Agents?
Meta — Introducing Muse: The World’s First Personal AI Agent Built for Everyone
